

Use a consistent assessment method
Record likelihood and impact through the same matrix, distinguish inherent from residual exposure, and document the controls considered.
ISO risk register
Maintain risks, controls, incidents, corrective actions, approvals, and review history in one system while your team builds and operates its management system.
No card required for the demo. Paid workspaces activate after checkout.
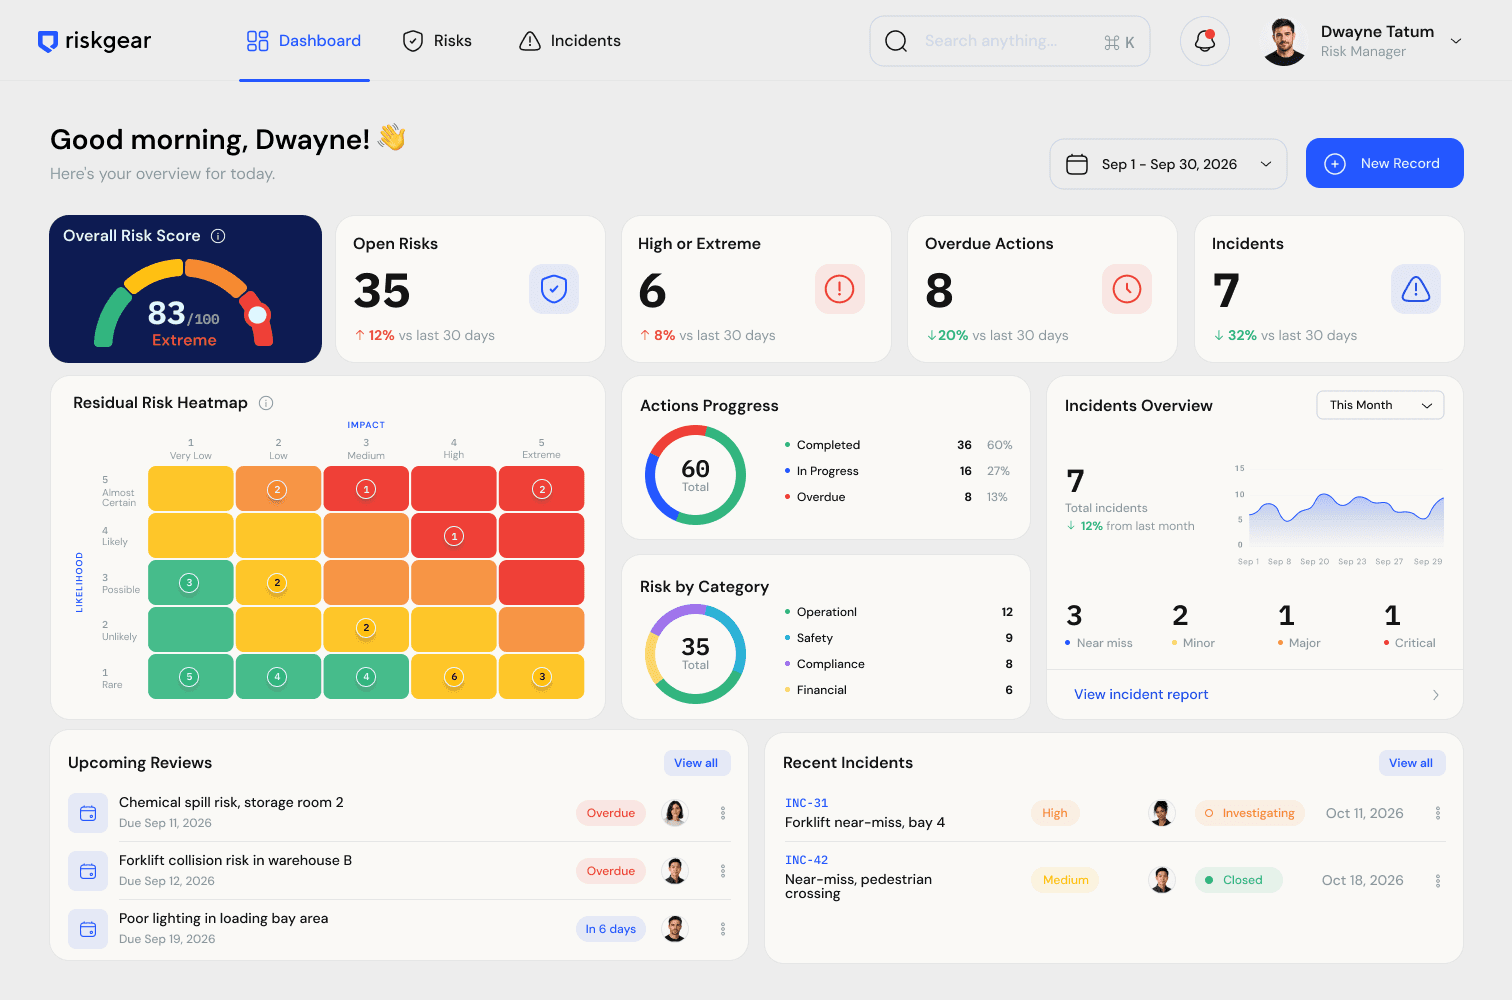
Teams preparing for ISO-related audits often have risk assessments, incident reports, action trackers, and evidence stored in different places. That fragmentation makes internal review slow and weakens the story behind each decision.
RiskGear brings those operational records together. It can support your preparation and evidence management, but it does not interpret a standard for you, replace professional advice, or guarantee conformity or certification.
What the system keeps together
Record likelihood and impact through the same matrix, distinguish inherent from residual exposure, and document the controls considered.
Keep ownership, reviews, approvals, actions, attachments, comments, and material history with each risk or incident record.
Link actual events to related risks and track the corrective work that follows an investigation.
Use dashboards and PDF reports to review current exposure and provide a controlled snapshot during an internal or external audit.
A practical workflow
Capture risks and incidents using consistent fields, categories, ownership, and status definitions.
Document existing controls, assess residual exposure, and assign further actions where needed.
Track due dates, approvals, comments, evidence, and changes as part of routine management review.
Export the relevant register and record reports for internal review or an external auditor.
Frequently asked questions
No. Certification is performed by an accredited certification body. RiskGear is software for maintaining risk, incident, action, approval, and evidence records that may support your management system.
RiskGear can help teams organise risk-based thinking, incident records, corrective actions, ownership, review dates, and documented evidence. Your organisation remains responsible for interpreting and meeting every applicable requirement.
Yes. Material record events such as creation, status and approval changes, comments, and actions are retained in the audit history.
Yes. PDF exports provide a readable snapshot of individual records or the wider register without requiring the auditor to access the live workspace.
Explore related workflows